What Is a .env File?
This is the first in a little series I'm doing on the different parts of a software application. The goal is simple: if you're getting into "vibe coding," building software by describing it to an AI, you shouldn't be completely in the dark about the pieces you're working with. So let's start with one you'll bump into almost immediately: the .env file.
First, why your app needs other programs
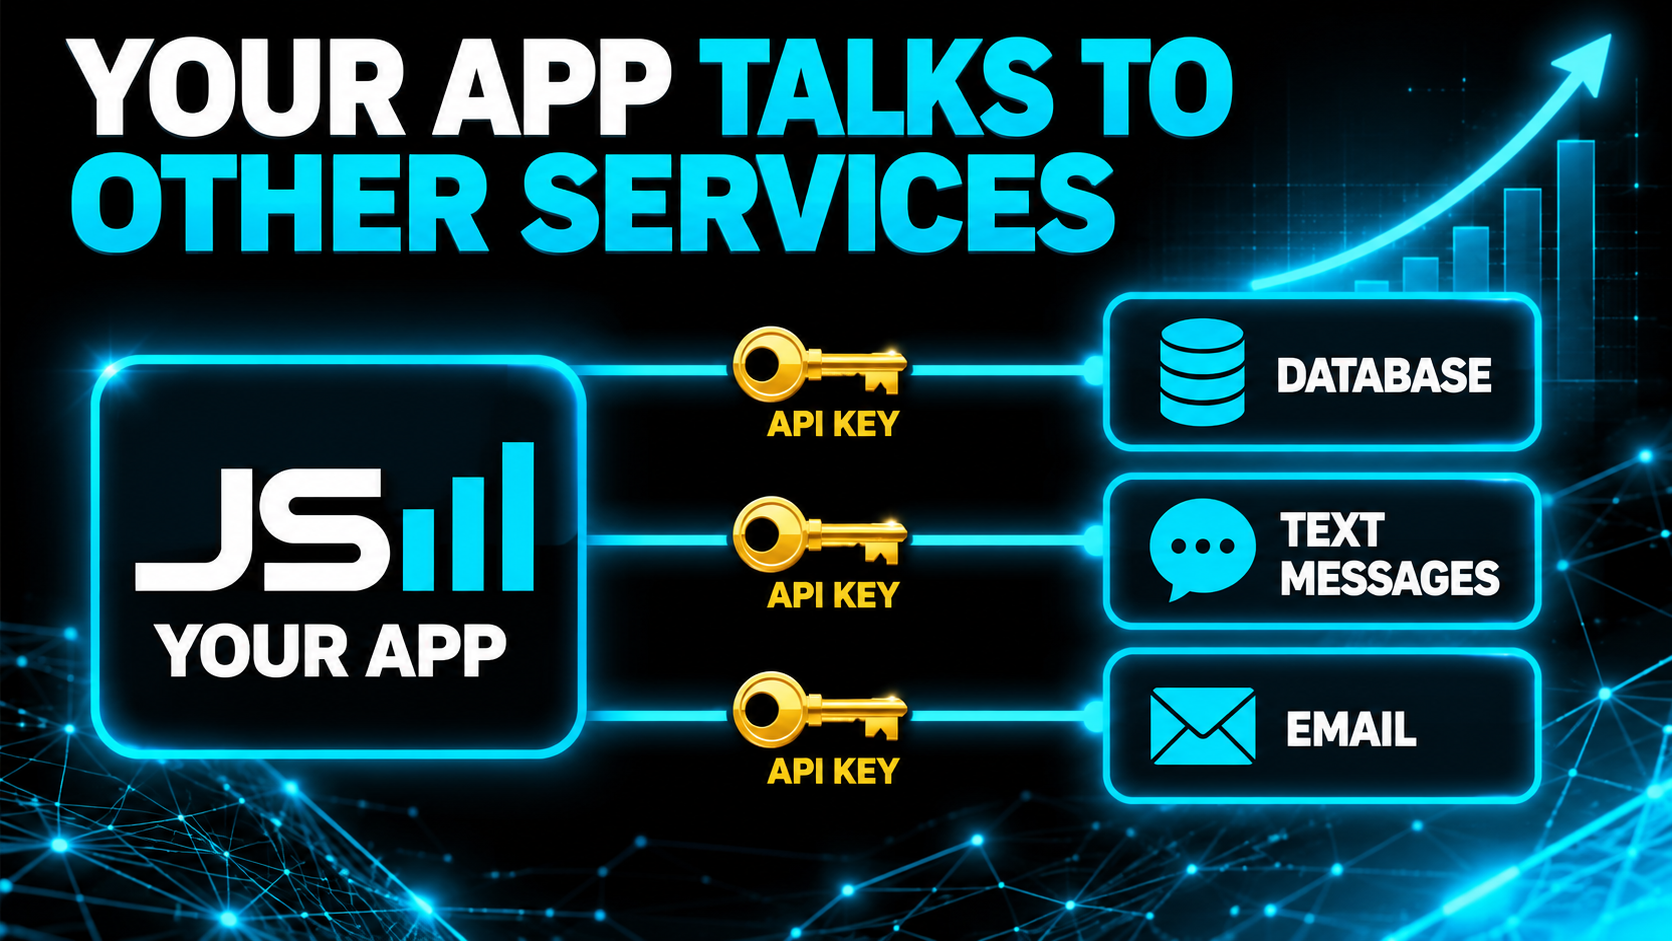
Almost no app does everything by itself. It leans on other programs and services, because that's just how software works. Take a CRM like our HyppoCRM. It needs:
- A backend database to store all its data. A CRM piles up a huge amount of data fast, so you need something real to hold it. (This, by the way, is exactly why Airtable is garbage as a backend, but that's another post.)
- A texting service like Twilio or Telnyx to send text messages. (Reviews on those two coming soon.)
- An email service like SendGrid, Postmark, or Mailgun to send emails.
So your one app is constantly talking to a handful of other services. And to talk to any of them, it needs a key.
What's an API key?
An API is just the doorway one piece of software uses to talk to another. An API key is the pass that gets your app through that doorway, it's how the service knows it's really you and lets your app in. Think of it like a password your program uses to log into another program.
And here's the catch: these keys are sensitive. If someone gets your key, they can run up your bill or worse, all while pretending to be you. So you do not want them lying around where they're easy to grab.
The wrong way, and the .env fix
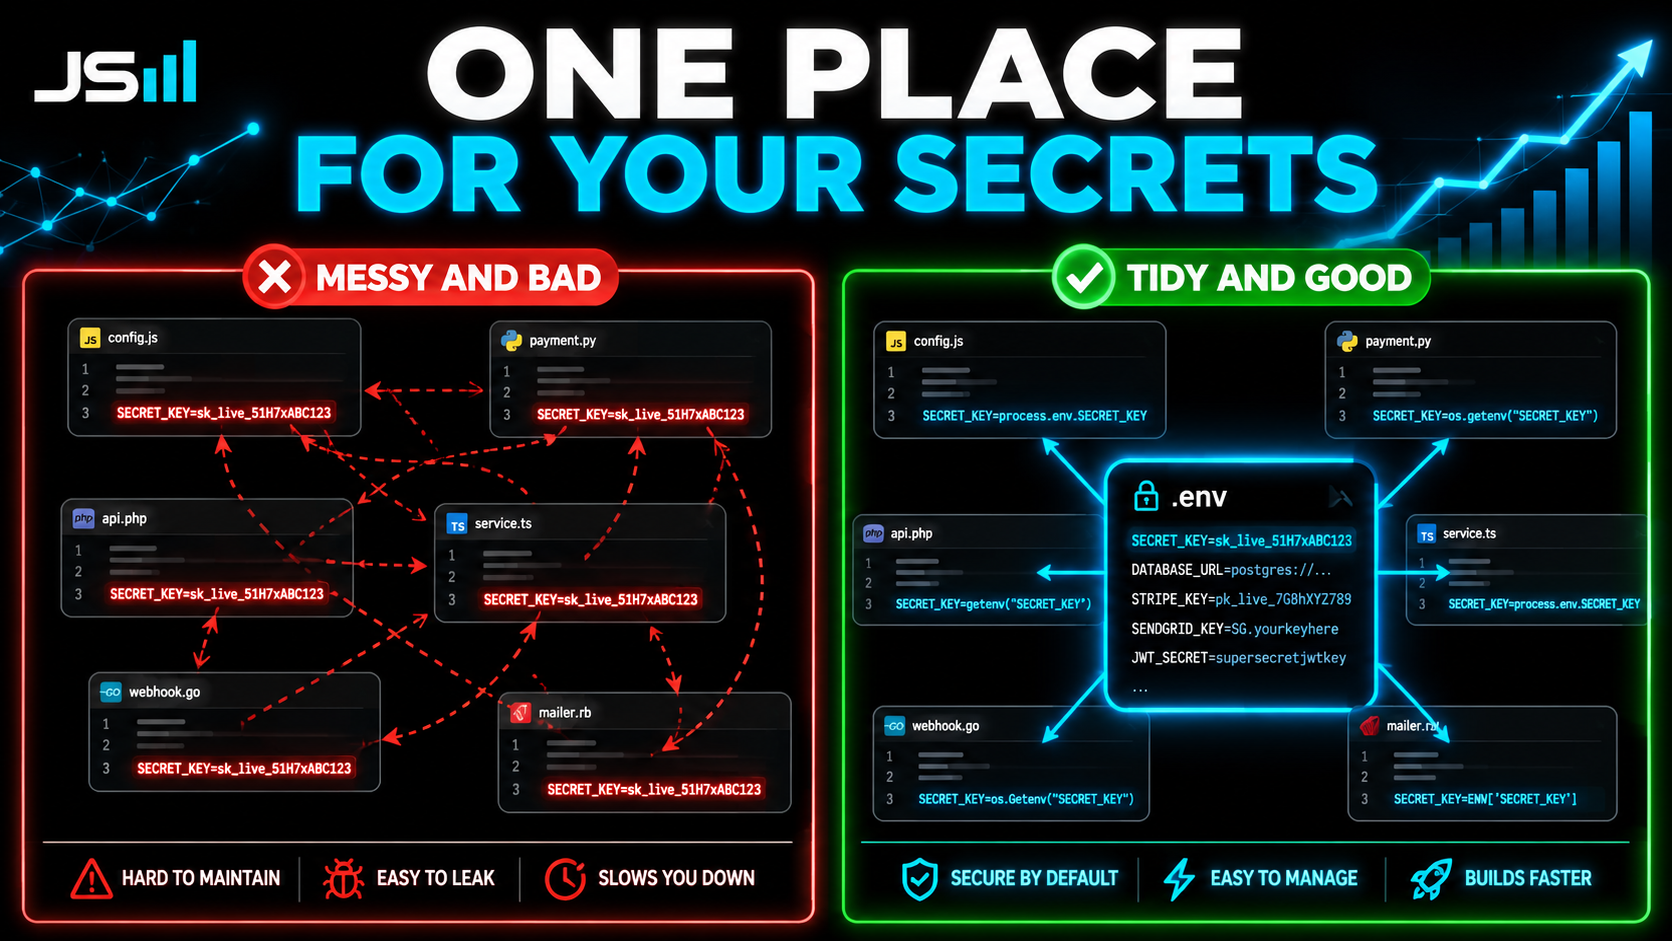
The naive approach is to paste the key directly into every spot in your code that uses it. That's a disaster for two reasons: it's easy to leak, and if it does leak, you have to hunt it down and change it in twenty different places.
Quick term: your codebase is just all the code that makes up your app, every file, all together. Now imagine sifting through that whole thing to swap out one leaked key. No thanks.
A .env file solves this. It's a single, private file where you keep all your secrets, your API keys, passwords, and credentials, in one place. Then, everywhere your code needs a key, instead of the raw key you put a reference to it, basically a labeled placeholder that says "go get the database key from the .env file." The real value lives in exactly one spot; the rest of your code just points at it.
Why this is the right way
Three clean wins:
- Easy to update. If a key leaks or you just want to rotate it, you change it in the .env file once. Every reference across your app instantly picks up the new value. One change instead of twenty.
- More secure. Your secrets live in one guarded place instead of being sprinkled all over your code where any leak exposes them.
- Good architecture. Fewer moving parts, one source of truth. As your app grows, that simplicity is exactly what keeps it from breaking. (I go deeper on this thinking in my piece On Architecture.)
One big rule: never commit it to GitHub
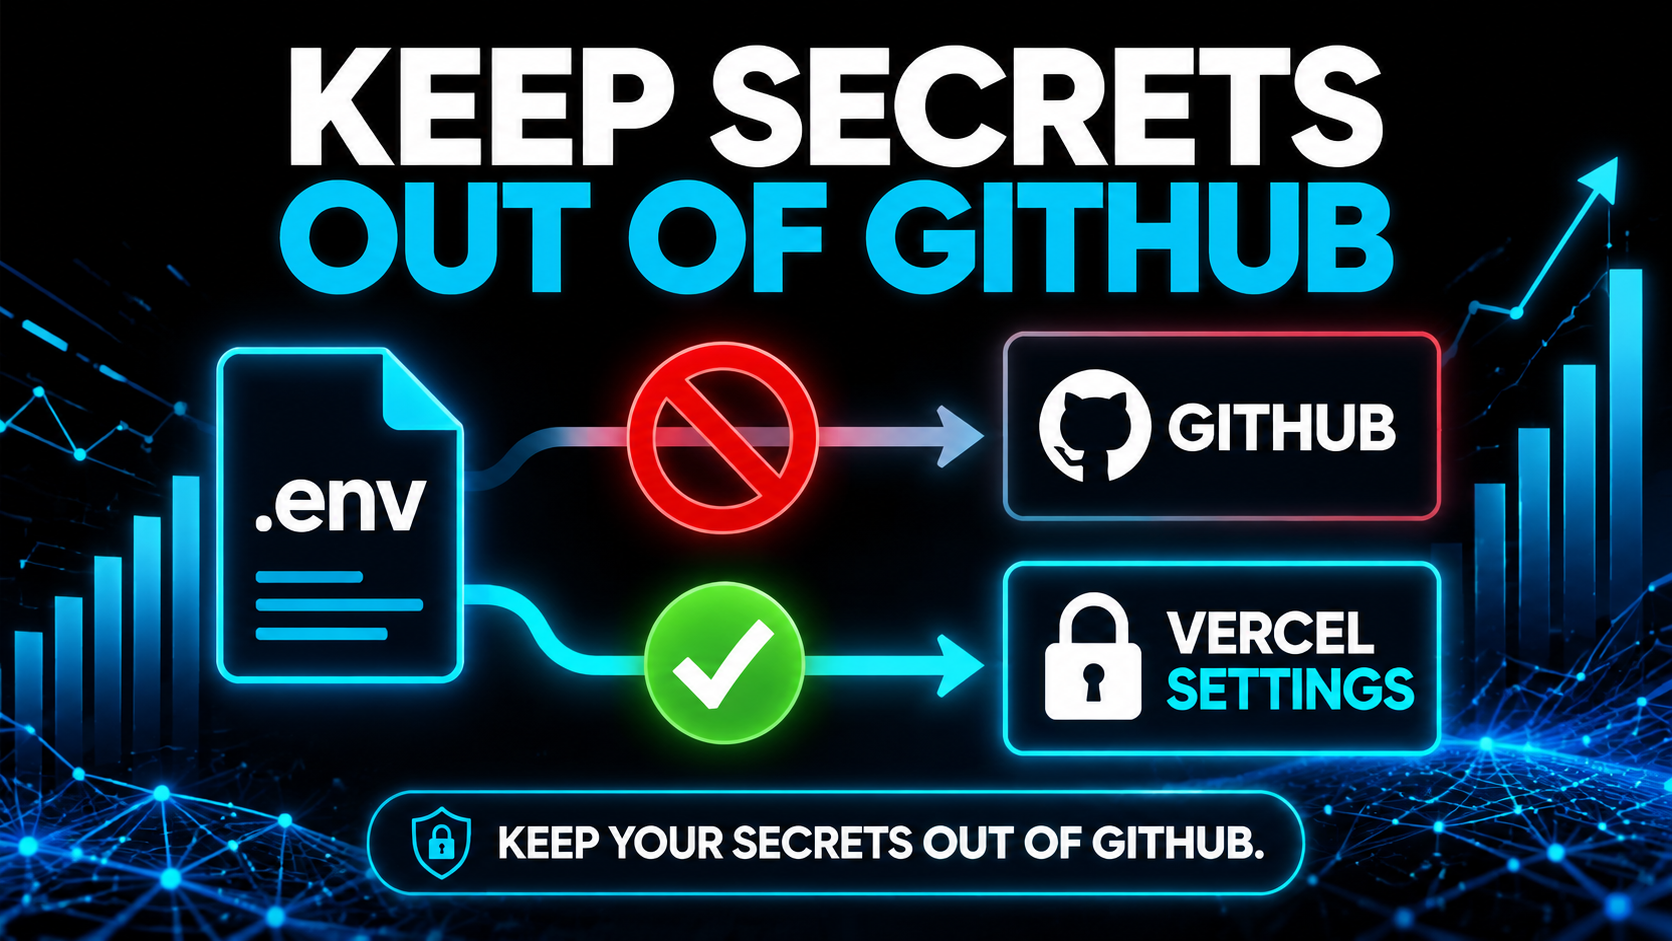
Last thing, and it's important. GitHub is where developers store and share their code online, think of it as the cloud home for your codebase. It's incredibly useful, but that's the problem: a lot of it is visible, and your secrets should never, ever be uploaded there. Commit your .env to GitHub and you've basically published your passwords.
Instead, when you deploy your app, store those values in your hosting platform's secure settings. If you're using Vercel, for example, there's a dedicated environment variables section for exactly this. Same idea as a .env file, kept safe and out of public view.
The takeaway
A .env file is just the locked drawer where your app keeps its secrets. Your app needs keys to talk to other services, those keys are sensitive, so you store them in one secure place, reference them everywhere else, and never let them touch GitHub. Simple concept, and getting it right early saves you a world of pain later.
That's one piece of the puzzle down. More parts of the application coming in this series.
Want software built right from the first file?
We build on solid foundations, secure, scalable, and done properly. That's what we do at HyppoAI.